Biography
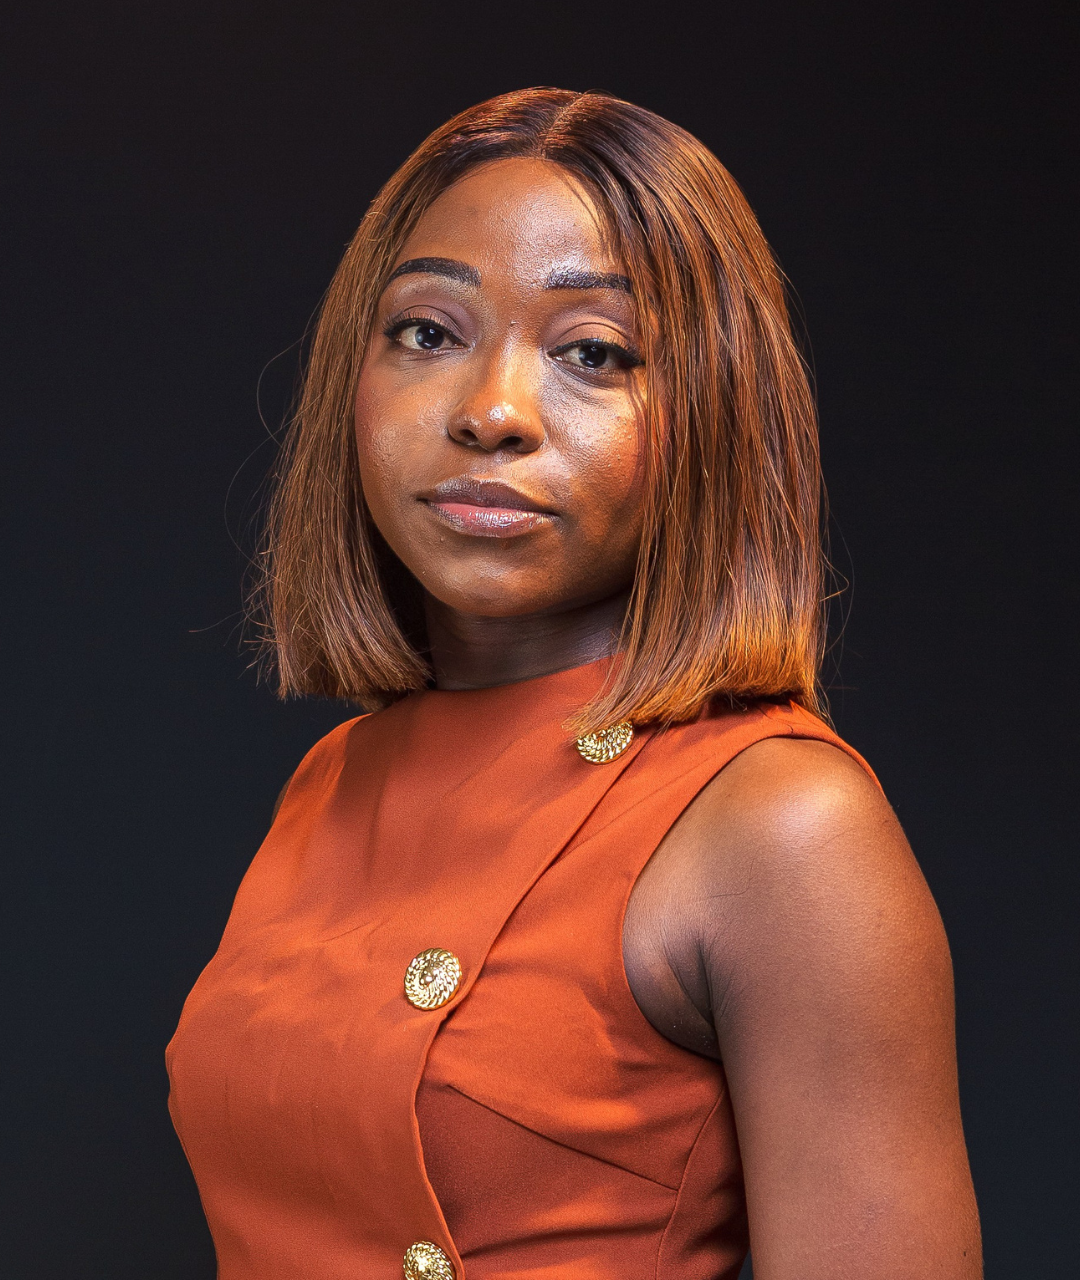
Oyindamola Omolara Ogunruku is an internal risk auditor with a Master of Science in Applied Statistics and Decision Analytics from Western Illinois University. I bring a quantitative and risk-focused perspective to internal audit, with experience supporting the evaluation of controls, operational processes, and data-driven decision-making. Oyindamola Omolara Ogunruku applies analytical and statistical methods to assess risk exposures, evaluate control effectiveness, and translate complex data into practical insights for management. My professional interests include internal audit, risk governance, data analytics, and the responsible use of emerging technologies, including artificial intelligence and cybersecurity governance. As a speaker, Oyindamola Omolara Ogunruku draws on this background to explore how organizations can strengthen risk management, improve decision-making, and build resilient operations through sound governance and evidence-based analysis.
Abstract
Title: Automation with Accountability : Managing AI-Enabled Cybersecurity and Operational Resilience.
Abstract: Artificial intelligence is increasingly used to support cybersecurity functions, including detecting suspicious activity, prioritizing alerts, assisting investigations, and supporting incident response. At the same time, AI systems can introduce security risks when models, training data, prompts, software components, or connected services are compromised, manipulated, or misused. This conceptual paper examines how organizations can pursue the benefits of AI-enabled cybersecurity while maintaining accountability, limiting harm, and preserving essential operations during disruption.
The paper focuses on three connected priorities. First, organizations should protect AI systems across their lifecycle, including secure development practices, data-integrity controls, access management, monitoring, and review of third-party dependencies. Second, automation should support rather than replace professional judgment. Human review, clear escalation procedures, and the ability to question or override automated recommendations remain important, particularly for consequential decisions and high-impact actions. Third, cybersecurity should extend beyond attack prevention to operational resilience. Organizations need tested response procedures, reliable backups, recovery plans, and personnel able to restore trustworthy operations when systems fail or are disrupted.
The discussion considers risks associated with data poisoning, adversarial manipulation, privacy breaches, and reliance on external technology providers. It also examines the role of secure development, access controls, continuous monitoring, staff training, and clear accountability in reducing exposure. These measures should be reviewed as technologies, threats, and operational requirements evolve.
The paper argues that resilience requires more than preventing attacks. It requires organizations to detect and contain incidents, preserve critical services, recover operations, and learn from failures. Collaboration among researchers, industry, and public institutions can support knowledge sharing and the development of safeguards that organizations with different resources can realistically adopt. The central argument is that a secure and resilient digital environment depends on combining AI capabilities with sound cybersecurity practice and responsible governance. The objective is not to eliminate all risk, but to reduce harm, maintain essential services, and restore reliable operations when failures occur.