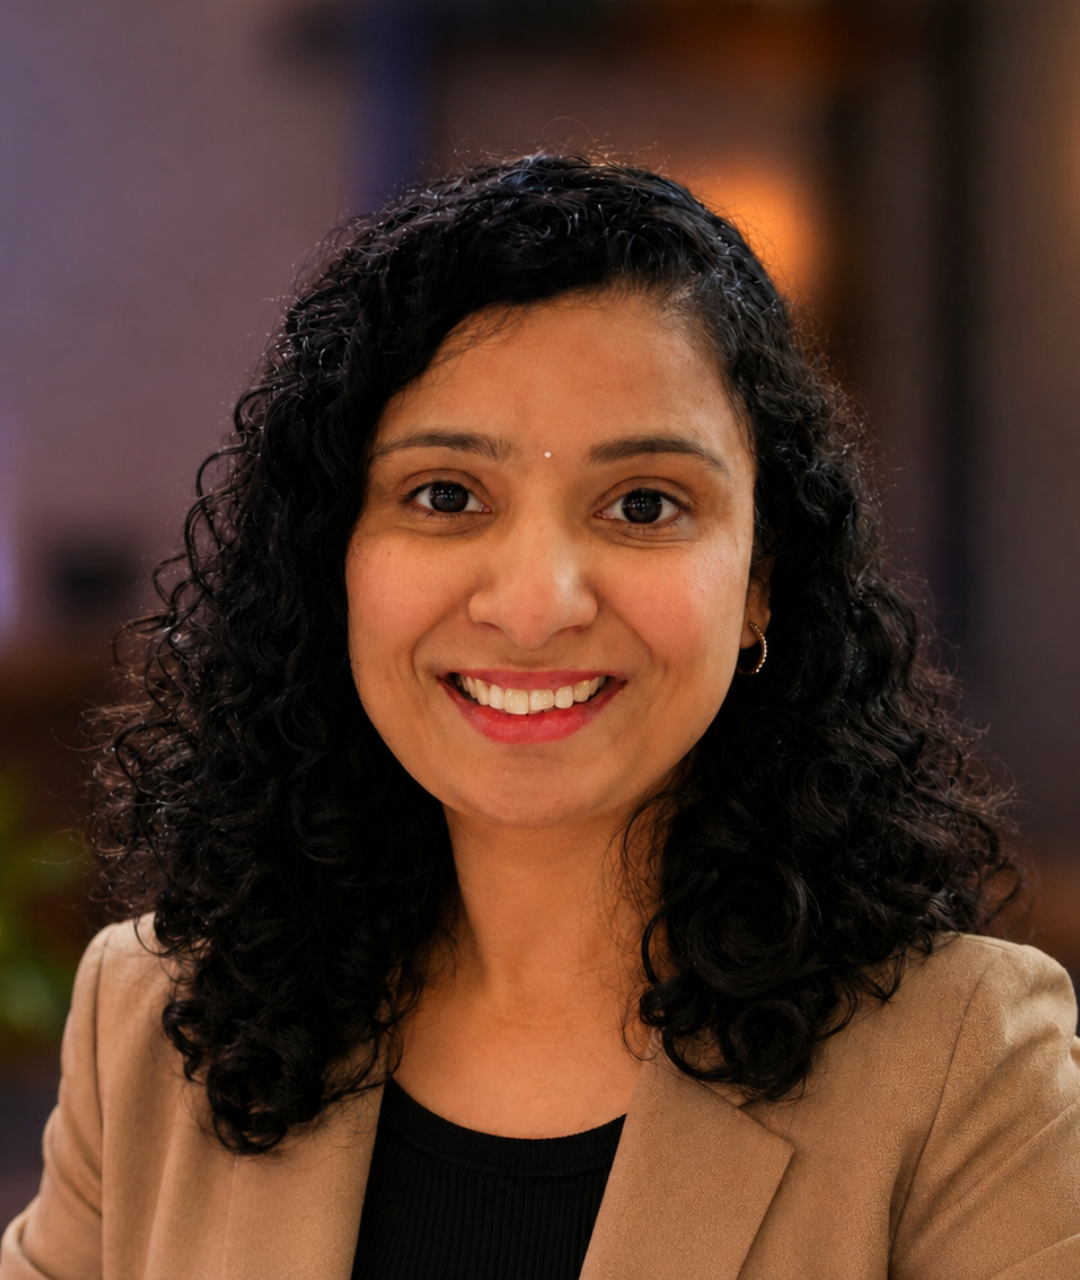Biography
Jothsna Pendyala is an AI and Platform Engineer, researcher, technical speaker, and Co-Founder of DeepAgentLabs. She specializes in generative AI, agentic systems, machine learning, cloud-native infrastructure, and reliable enterprise AI platforms. Her expertise spans retrieval-augmented generation, agent orchestration, Kubernetes, and AI deployment across Azure and AWS.
At DeepAgentLabs, she contributes to an open-source ecosystem focused on building observable, reliable, resilient, and governable AI systems for production. Her work combines LangGraph, Model Context Protocol (MCP), evaluation, observability, and responsible AI practices to support enterprise automation and AI-assisted operations.
Her research contributions include work published through NeurIPS, IEEE, and Springer. Through research, technical talks, and open-source contributions, Jothsna connects practical AI engineering with the challenges of designing, deploying, and operating dependable AI systems
Abstract
Title: Who Secures the Security Agent? Zero Trust for AI-Driven Vulnerability Remediation
Abstract: AI agents can help engineering teams investigate security findings and propose code fixes. To do this, they need access to repositories, scanners, and development tools. That access creates a critical security problem: the agent tasked with removing a vulnerability can introduce an unsafe change, expose sensitive information, or follow malicious instructions embedded in repository content. A successful scan does not establish that the remediation process itself is trustworthy.
This presentation examines how zero trust principles can govern AI-driven vulnerability remediation. Drawing on hands-on experience with enterprise agentic platforms, secure delivery pipelines, and access controls, it presents a reference workflow in which a scanner identifies a
weakness, an agent proposes a patch, and independent controls determine whether the change can proceed.
The workflow separates repository content from trusted instructions, grants task-scoped access, and isolates patch execution from production systems. Static analysis, dependency checks, and relevant tests validate proposed changes before policy checks and human review permit merging or deployment. The agent can recommend a fix without having unrestricted authority to approve or release it.
A worked example follows a security finding through investigation, patch generation, and validation. Adversarial scenarios examine whether misleading repository instructions, requests for broader permissions, and unsafe proposed changes are blocked. The session distinguishes code vulnerability detection from the controls needed to secure the agent performing remediation.
Attendees will learn where to place trust boundaries and approval gates, what evidence to retain for review, and how to evaluate a remediation workflow for both patch quality and unauthorized actions.